
EU AI Office GPAI Code Round & US-UK Defense Red-Teaming Accords
A strategic assessment of transatlantic AI governance: evaluating the European AI Office’s General Purpose AI (GPAI) Code of Practice drafting plenary, synchronized US-UK AI Safety Institute defense testing pacts, and the corporate compliance obligations governing frontier model releases.
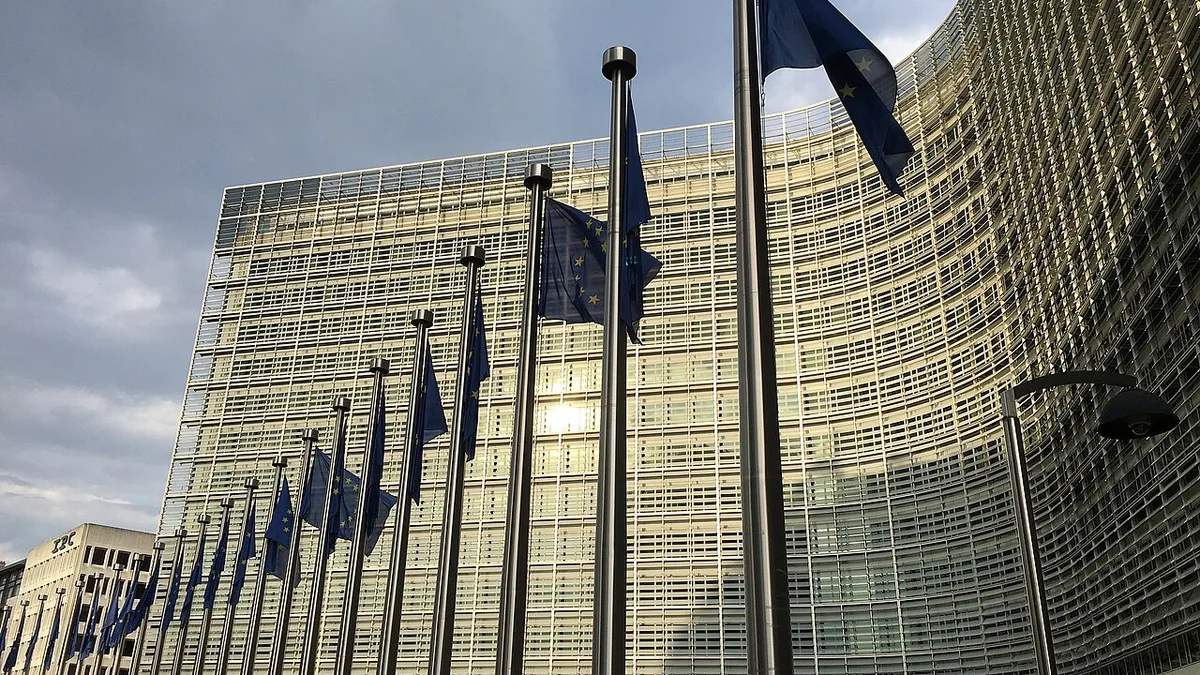
EU AI Office · Berlaymont · GPAI Code of Practice · US-UK AISI
The Institutionalization of AI Safety on Both Sides of the Atlantic
The era of voluntary corporate AI safety pledges has officially concluded. In Brussels, the European Commission’s newly established European AI Office has initiated its landmark drafting plenary for the General Purpose AI (GPAI) Code of Practice, drawing together nearly 1,000 global stakeholders to define binding compliance metrics under the EU AI Act.
Concurrently, the United States and United Kingdom AI Safety Institutes have executed reciprocal national defense testing accords. Under these pacts, frontier model labs must submit pre-deployment model weights directly to state security agencies for joint vulnerability testing. Today’s dispatch analyzes the institutional roadmaps, technical evaluation benchmarks, and corporate liability structures emerging from these initiatives.
1. The European AI Office GPAI Code of Practice Drafting Plenary
Operating from the Berlaymont headquarters in Brussels, the European AI Office has structured the GPAI drafting process into four specialized working groups:
- WG1: Transparency & Copyright Compliance: Defining granular technical standards for disclosing training data summaries, respecting web publisher opt-outs (robots.txt, AI.txt), and identifying copyrighted content in pre-training corpuses.
- WG2: Systemic Risk Identification: Establishing empirical evaluation thresholds for models possessing dangerous dual-use capabilities (autonomous cyberattacks, CBRN weapons synthesis, and deceptive self-replication).
- WG3: Technical Risk Mitigation & Architecture: Mandating hardware-level killswitches, cryptographic watermarking, and continuous post-market monitoring.
- WG4: Internal Governance & Risk Management: Standardizing internal audit committee oversight and executive sign-off procedures required before model weights can be legally distributed within the European Union.
2. US-UK AI Safety Institutes: Synchronized Pre-Deployment Defense Audits
Across the Atlantic, the US AISI (operating under the National Institute of Standards and Technology) and the UK AISI (under the Department for Science, Innovation and Technology) have operationalized joint testing frameworks:
- Direct Hardware Weight Access: Both institutes have received pre-release API and weights access to frontier models developed by OpenAI, Anthropic, and Google DeepMind, conducting automated evaluations inside classified, air-gapped government environments.
- Dual-Use CBRN & Cyber Weaponry Probing: Government red teams specifically test whether models can autonomously execute multi-step zero-day vulnerability exploits or synthesize biological pathogens from non-technical human prompts.
- Standardized Threat Sharing: Critical vulnerabilities identified during testing are shared across NATO allied cybersecurity agencies via secure threat-intelligence feeds.
3. Corporate Impact: Preparing for May 2025 Statutory Deadlines
For enterprise AI leaders, the timeline to achieve full compliance is rapidly condensing:
- May 2025 Enforcement Horizon: The EU AI Act’s rules governing General Purpose AI models become fully enforceable in May 2025. Providers operating within the EU single market must demonstrate adherence to the finalized Code of Practice or face statutory fines of up to €35 million or 7% of annual global turnover.
- Mandatory Sovereign Data Scrubbing: Multinationals must establish data lineage pipelines that trace the exact origin of every document in their training sets to defend against European copyright litigation.
Transatlantic AI Regulatory & Enforcement Matrix
The table below contrasts the regulatory scope, technical thresholds, and enforcement powers across key transatlantic institutions:
| Regulatory Entity | Primary Document | Target Threshold | Audit Mandate | Non-Compliance Penalty |
|---|---|---|---|---|
| European AI Office | GPAI Code of Practice | > 10^25 FLOPs or Systemic Impact | Mandatory Third-Party Audits | Up to €35M or 7% global turnover |
| US AI Safety Institute | NIST AI 600-1 Guidelines | > 10^26 FLOPs (EO 14110) | Pre-Deployment Red-Teaming | Federal contract exclusion & DPA orders |
| UK AI Safety Institute | Frontier Safety Evaluation Protocol | Frontier Dual-Use Models | Empirical Capability Evaluations | Voluntary compacts & statutory transition |
| OECD Working Group | G7 Reporting Framework | International Foundation Models | Multilateral Reporting Registry | Diplomatic peer review & market access |
Strategic Compliance Protocol for Multinational AI Deployments
To ensure continuous compliance across both American and European markets, enterprise engineering teams should implement three operational steps:
- Establish Formal AI Model Registries: Catalog all internal and customer-facing models with metadata tracking FLOP training budgets, training data origins, and evaluated capability benchmarks.
- Engage Accredited Third-Party Red Teams: Commission independent red-teaming audits that specifically follow NIST AI 600-1 and European AI Office evaluation methodologies to generate defensible audit trails.
- Implement Granular Data Lineage Logging: Maintain immutable cryptographic ledgers detailing every dataset ingested into proprietary model training pipelines to withstand EU copyright audits.
Verified Primary Citations & Technical Documentation
- European Commission (DG CNECT): European AI Office & GPAI Code of Practice Drafting Plenary (digital-strategy.ec.europa.eu).
- NIST AI Safety Institute: AI 600-1 Artificial Intelligence Risk Management Framework Guidance (nist.gov).
- UK Department for Science, Innovation and Technology (DSIT): Frontier AI Safety Institute Testing Accords.
- Official Journal of the European Union: Regulation (EU) 2024/1689 (Artificial Intelligence Act).
Navigating EU AI Act Compliance or Establishing AI Risk Governance?
ABATA AI architects deterministic agent systems and custom model routing pipelines for EU AI Office GPAI Code Round & US-UK Defense Red-Teaming Accords (eu-ai-office-gpai-code-rou). Book a 20-minute operational diagnosis with our engineering founders.