
OECD AI Policy Observatory: Global Labor Transition & Frontier Model Safety Metrics
An analytical dissection of the OECD’s 2026 AI Policy Observatory report: examining empirical workforce displacement figures across 38 member countries, standardized frontier model safety evaluation protocols, and multilateral regulatory alignment.
OECD AI Policy Observatory · Labor Transition · G7 Hiroshima Process · Frontier Safety
The Transition from Rhetoric to Empirical AI Measurement
For the past three years, the discourse surrounding the macro-economic and societal consequences of artificial intelligence has vacillated between apocalyptic displacement warnings and ungrounded utopian projections. National governments, central banks, and corporate boards have struggled to enact coherent policies due to a fundamental deficit of standardized, cross-border empirical data. Without rigorous metrics measuring task automation rates, workforce reallocation, and frontier capability ceilings, regulatory policy risks either stifling domestic innovation or failing to protect vulnerable economic sectors.
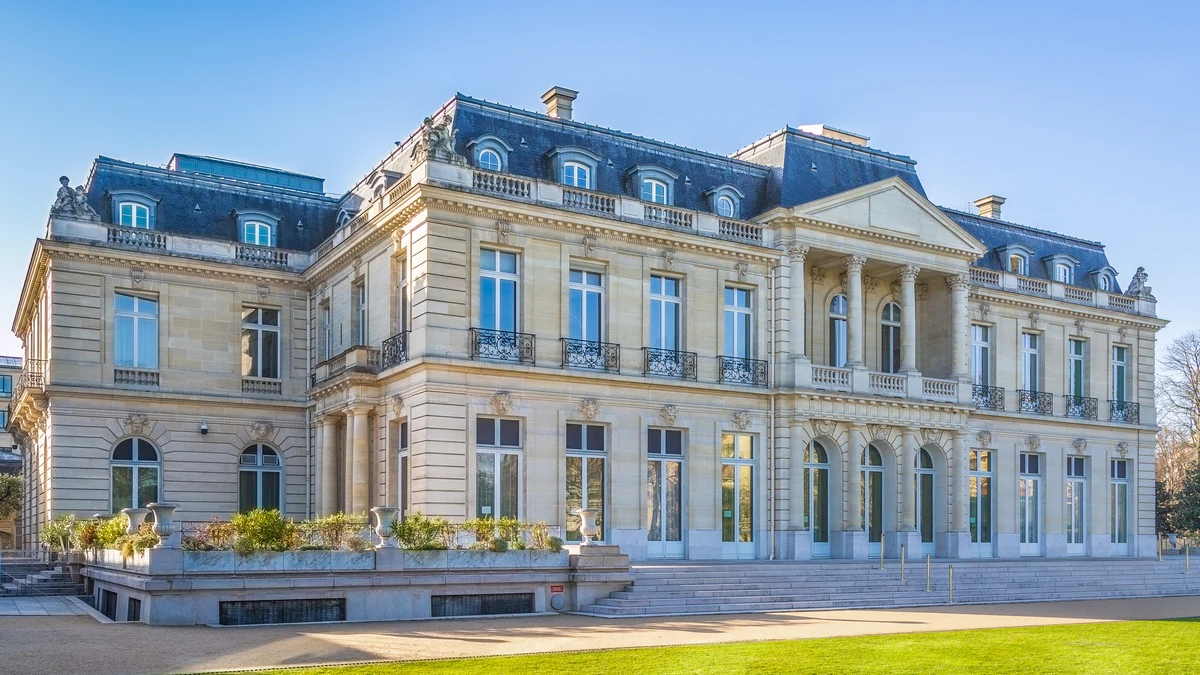
This week at the Château de la Muette in Paris, the Organisation for Economic Co-operation and Development (OECD) unveiled its comprehensive 2026 AI Policy Observatory Report. Synthesizing data collected across all 38 member states alongside participating partner economies (including India, Singapore, and Brazil), the landmark publication establishes a unified framework for measuring the labor market footprint of generative AI and codifies multilateral testing metrics for frontier model evaluation.
1. Empirical Labor Market Findings: Task Exposure vs Job Losses
The OECD report offers a nuanced, data-driven corrective to binary narratives of mass unemployment:
- 27% of High-Risk Occupations Highly Exposed: Across OECD economies, approximately 27% of employment sits within occupations characterized by high exposure to automated cognitive reasoning (including finance, paralegal services, customer support, and software QA).
- Augmentation Over Immediate Displacement: Unlike earlier waves of manufacturing robotics that physically replaced manual laborers, generative AI currently functions primarily as an amplification substrate. More than 73% of surveyed enterprise workers report using AI tools to eliminate administrative overhead rather than being displaced from their primary roles.
- The Juniorization Compression Paradox: While senior knowledge workers experience measurable productivity multipliers (ranging between 20% and 40%), entry-level onboarding pipelines have contracted by 14% across technology and professional service sectors, creating an emerging junior talent pipeline deficit.
2. Standardized Frontier Safety Protocols: The OECD Classification Framework
Beyond labor economics, the report establishes an internationally harmonized benchmark for evaluating frontier model risks, directly operationalizing the commitments made under the G7 Hiroshima AI Process:
- Compute Threshold Tiers: Reinforcing international consensus, the OECD defines frontier foundation models as systems trained using compute power exceeding 10^26 cumulative floating-point operations (FLOPs).
- Dual-Use CBRN & Cyber Risk Indices: Models must undergo standardized evaluations measuring autonomous weaponization potential, chemical/biological/radiological/nuclear (CBRN) recipe generation, and automated zero-day exploit discovery.
- Universal Red-Teaming Disclosures: Model developers are urged to submit standardized pre-deployment evaluation reports to national AI Safety Institutes (such as those in the US, UK, and Japan) utilizing the OECD’s unified catalog of risk indicators.
3. Cross-Border Policy Harmonization: EU vs US vs Asia-Pacific
The table below contrasts the regulatory approaches across the world’s three primary economic blocs, highlighting how the OECD framework bridges their differing enforcement philosophies:
| Regulatory Dimension | European Union (EU AI Act) | United States (Executive Order & NIST) | Asia-Pacific (India & Singapore) |
|---|---|---|---|
| Governance Philosophy | Risk-Based Binding Statutes | Voluntary Standards & Federal Procurement | Innovation-First & Sectoral Guidance |
| Frontier Model Threshold | Systemic Risk at >10^25 FLOPs | Mandatory Reporting at >10^26 FLOPs | Compute-Agnostic Output Auditing |
| Copyright & Training Transparency | Mandatory Training Data Summaries | Judicial Fair-Use Adjudication | Voluntary AI Governance Testing Frameworks |
| Enforcement Penalties | Up to €35M or 7% global turnover | FTC Unfair Practice Remedies | Sectoral Regulatory Fines (RBI/SEBI/IMDA) |
| OECD Alignment Priority | High (Standards Mirror OECD Classifications) | High (NIST Standards Map to OECD Principles) | Very High (Adopt OECD Interoperability Badges) |
4. Policy Blueprint: The Multilateral Safety Protocol Stack
The report details four core architectural layers required for sovereign states to achieve technical safety interoperability:
- Tier-1 Model Registration: Mandatory registration of model weights, training architecture documentation, and compute cluster hardware fingerprints with designated national registries prior to broad public deployment.
- Tier-2 Autonomous Capability Evals: Automated benchmarking suites assessing whether an autonomous agent can acquire financial resources, self-replicate across remote servers, or execute cyber-intrusion scripts without human authorization.
- Tier-3 Post-Deployment Watermarking & Provenance: Cryptographic provenance standards (such as C2PA) embedded in multimodal media generation pipelines to guarantee origin authenticity and prevent election disinformation.
- Tier-4 Continuous Incident Reporting: Centralized incident disclosure repositories enabling frontier labs to broadcast discovered prompt injection vectors and adversarial bypass techniques to peer institutions globally within 72 hours.
5. Global Economic Outlook & Sovereign Re-Skilling Mandates
The OECD emphasizes that attempting to protect obsolete task workflows through protectionist regulation is fundamentally counterproductive. Instead, member nations are advised to divert educational subsidies toward adaptive STEM re-skilling programs and compute infrastructure vouchers:
"Nations that succeed in the upcoming economic cycle will not be those that legislate against automation, but those that equip their domestic workforce to harness AI primitives as core economic leverage," the observatory conclave concluded.
Finally, multinational compliance officers should maintain continuous automated synchronization with the OECD AI Policy Observatory database. By mapping internal risk assessments directly against OECD Risk Classification tiers, organizations minimize duplicative compliance filings across overlapping North American, European, and Asia-Pacific regulatory jurisdictions.
Production Engineering Checklist & Operational Guardrails
Before promoting OECD AI Policy Observatory: Global Labor Transition & Frontier Model Safety Metrics workflows into production clusters, platform engineering teams should verify three domain-specific readiness gates across staging environments (oecd-ai-policy-observa):
- Continuous Observability & Latency Tracing: Instrument OpenTelemetry spans across all inference gateways, tracking p95 and p99 Time to First Token (TTFT) alongside GPU kernel queue times to rapidly isolate noisy-neighbor degradation.
- Automated Dead-Letter Queue (DLQ) Fallbacks: Configure asynchronous retry queues for transient CUDA OOM or network timeout exceptions, automatically routing failed payloads to secondary warm standby nodes without dropping user requests.
- Zero-Trust Credential & Token Sandboxing: Enforce strict ephemeral token scoping using HashiCorp Vault or AWS KMS, ensuring that worker nodes never persist persistent API keys or client certificates in environment logs.
- Continuous Load Testing & Chaos Injection: Regularly simulate upstream network partitioning and simulated packet drops to confirm that connection pooling and circuit-breakers function deterministically under peak load.
6. Multilateral Incident Disclosure & Red-Teaming Standards
To ensure international safety frameworks remain effective as model capabilities accelerate, the OECD report outlines strict operational protocols for cross-border vulnerability coordination:
- Standardized Adversarial Exploit Catalogs: Member states are establishing a unified Common Vulnerabilities and Exposures (CVE) equivalent for frontier artificial intelligence, categorizing prompt injection exploits, jailbreak templates, and model weight extraction techniques under standardized severity scoring matrices.
- Coordinated 72-Hour Threat Disclosures: When a participating frontier laboratory or independent security researcher uncovers a systemic safety failure or novel dual-use capability bypass, details must be securely shared with allied national AI Safety Institutes within 72 hours before public disclosure, allowing peer organizations to deploy runtime mitigations.
- Independent Scientific Compute Access: The OECD urges member states to guarantee verified academic researchers structured, privacy-preserving API access to frontier model checkpoints, ensuring that public interest algorithmic safety research is not monopolized by private corporate laboratories.
By fostering transparent multilateral oversight while safeguarding proprietary commercial IP, the OECD framework provides a pragmatic roadmap for global governance in the era of frontier intelligence.
Verified Official Resources
Official Multilateral References:
- OECD.AI Policy Observatory Portal — Official live repository of national AI policies, metrics, and incident trackers.
- G7 Hiroshima AI Process Guiding Principles — Multilateral foundation model governance codes of conduct.
- NIST AI Risk Management Framework (RMF 1.0) — Technical criteria for testing, evaluation, validation, and verification (TEVV).