
The Transatlantic AI Divide: EU GPAI Code of Practice Clashes with US Compute Accords
As the European AI Office prepares to finalize its General-Purpose AI (GPAI) Code of Practice, sharp ideological and regulatory divisions are emerging between European regulators and US-allied compute coalitions.
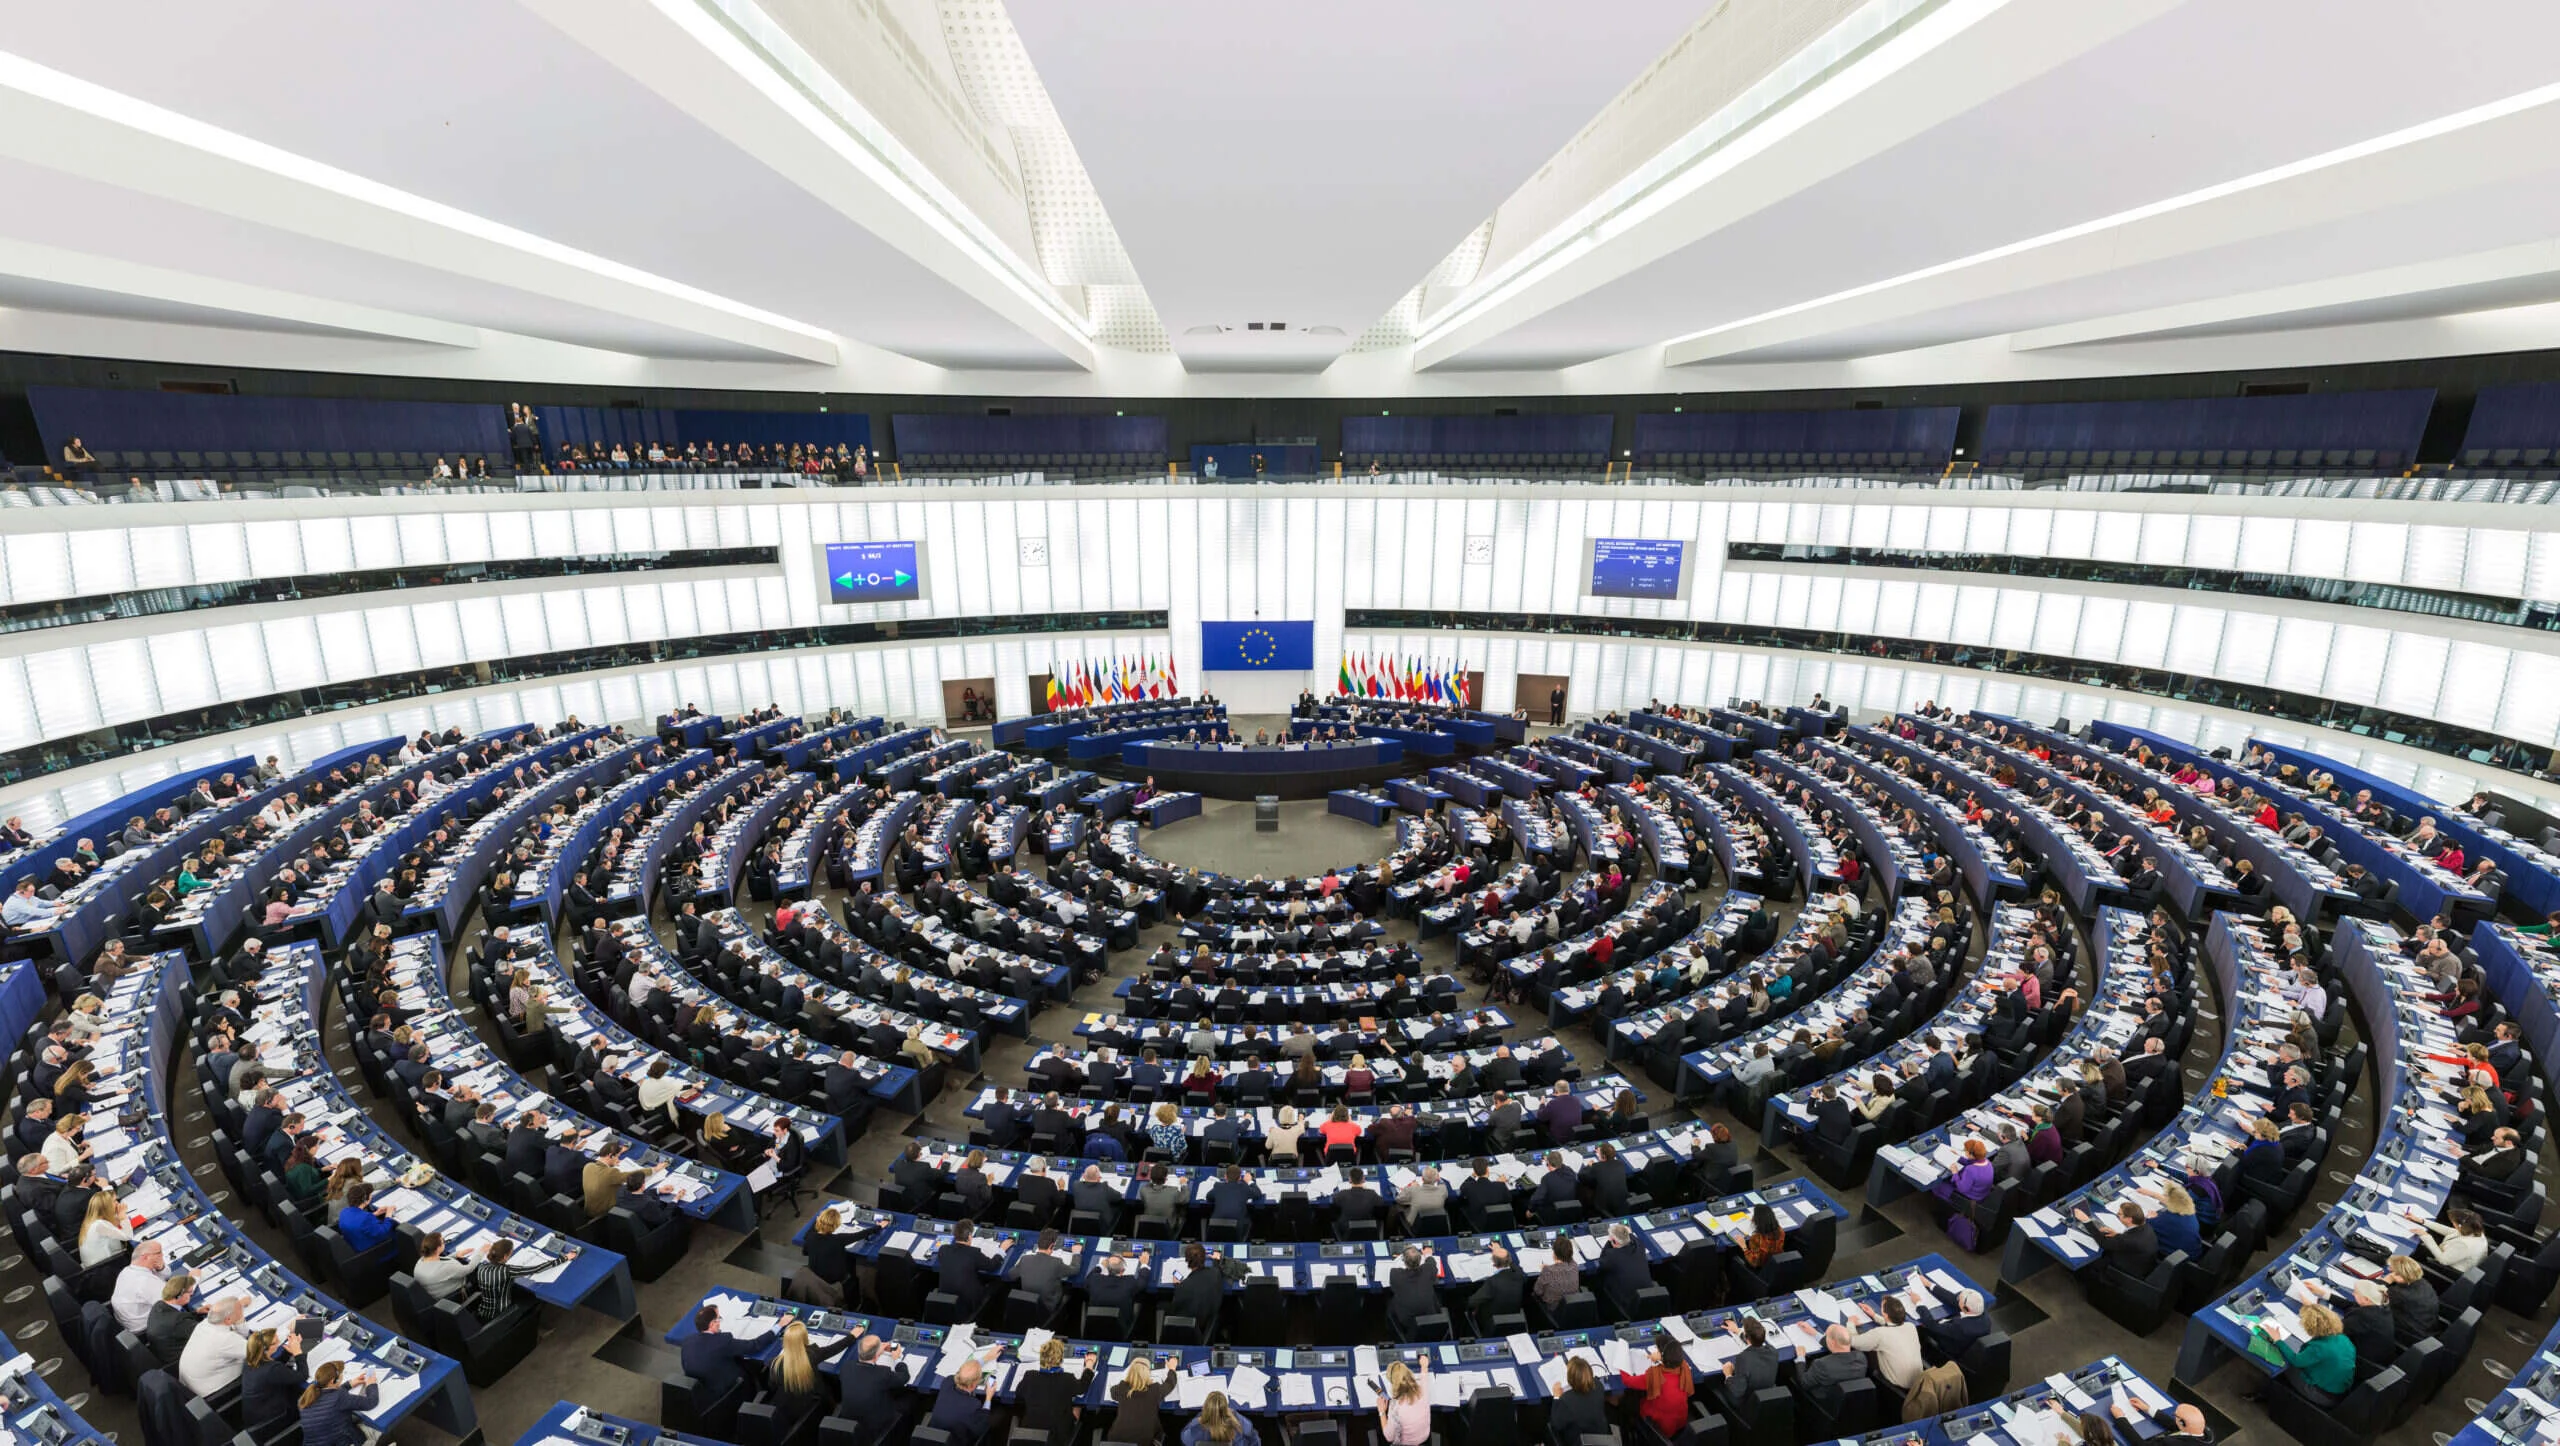
A Tale of Two Regulatory Philosophies
Over the past three years, the global governance of artificial intelligence has split into two distinctly irreconcilable philosophical camps. On the western side of the Atlantic, the United States alongside allies Japan and the United Kingdom has pursued an empirical, capability-driven governance model anchored by national AI Safety Institutes, voluntary developer preparedness frameworks, and multilateral compute-sharing pacts.
On the eastern side of the Atlantic, the European Union has pursued comprehensive, statutory codification. Anchored by the landmark EU AI Act entered into force in 2024, European governance treats frontier models through a formal product-safety framework backed by legally binding transparency mandates, statutory conformity assessments, and substantial financial fines reaching up to €35 million or 7% of global annual turnover.
On October 16, 2026, this philosophical divergence escalated into open regulatory confrontation. As the European AI Office convened plenary drafting sessions in Brussels to finalize the General-Purpose AI (GPAI) Code of Practice, American technology executives and European policymakers clashed over model weight transparency, copyright data disclosures, and mandatory safety audits.
Inside the GPAI Code of Practice: The Contested Compliance Pillars
The GPAI Code of Practice represents the operational rulebook translating the abstract statutory requirements of Articles 51 through 55 of the EU AI Act into enforceable technical standards. The drafting dispute centers on three fiercely contested pillars:
First, the European AI Office demands comprehensive public documentation detailing all copyrighted data sources, crawl repositories, and licensing arrangements utilized during pre-training. American frontier developers argue that disclosing granular dataset inventories would expose trade secrets to foreign competitors and trigger an avalanche of speculative copyright litigation.
Second, the draft code establishes mandatory third-party safety red-teaming conducted exclusively by European accredited audit bodies. Under proposed rules, auditors would possess statutory authority to inspect raw model weights, gradient checkpoints, and internal reinforcement learning alignment traces prior to commercial deployment within the European single market.
Third, the code enforces strict systemic risk classifications based on floating-point operation (FLOP) thresholds (10^25 FLOPs) alongside qualitative capability evaluations. Models categorized as systemic risks face ongoing energy consumption reporting, cybersecurity penetration testing, and mandatory incident notification obligations within 72 hours of an anomaly.
American Resistance: Intellectual Property and National Security Concerns
Representatives from leading American AI developers and the US Department of Commerce voiced vigorous opposition during the Brussels proceedings. In a joint submission, industry leaders argued that requiring American technology firms to surrender proprietary model weights and training logs to European auditors poses unacceptable intellectual property and national security risks.
US officials highlighted that under recently signed trilateral accords with the UK and Japan, frontier model evaluation is conducted within cryptographically sealed hardware enclaves (the Global AI Safety Cloud) that protect developer IP while rigorously verifying safety. American negotiators cautioned that intrusive European inspection mandates could force US frontier labs to withhold next-generation releases from the European market.
Furthermore, Silicon Valley venture capital leaders warned that heavy compliance costs would crush early-stage AI startups while cementing an oligopoly of well-capitalized hyperscalers capable of financing armies of European compliance lawyers.
The European Counter-Argument: Democratic Accountability and Digital Sovereignty
European lawmakers and civil society organizations vigorously defended the Code of Practice, framing it as a vital defense of democratic accountability and fundamental human rights. European officials pointed out that voluntary corporate self-regulation has repeatedly failed in consumer privacy, social media moderation, and environmental protection.
Members of the European Parliament emphasized that the European Union represents an affluent single market of 450 million consumers that no commercial enterprise can afford to abandon. By establishing rigorous standards for copyright transparency and systemic risk auditing, Europe aims to prevent multinational technology monopolies from appropriating human intellectual property without fair compensation.
European foundation model pioneers, notably Mistral AI in France and Aleph Alpha in Germany, have actively participated in drafting the code. Having designed their open-weight architectures (such as Mistral Large 4) to be GDPR-compliant and auditable by design, domestic European champions view strict statutory standards as a competitive advantage against closed American cloud APIs.
The Market Balkanization Threat: Geo-Blocking and Delayed Feature Rollouts
The practical consequence of this transatlantic regulatory standoff is the growing balkanization of the global artificial intelligence market. Over the past twelve months, major American technology providers have repeatedly delayed or withheld advanced multimodal and agentic features from European users.
European consumers and enterprises have experienced staggered rollouts for multimodal voice agents, real-time computer vision capabilities, and autonomous desktop action tools due to regulatory uncertainty under the AI Act and GDPR. If the GPAI Code of Practice adopts maximalist disclosure rules, industry analysts warn that several US frontier labs may geo-block upcoming 2027 flagship models within the European Union entirely.
Such a bifurcation would create significant productivity disparities, leaving European enterprises operating on older foundation models while American, British, and Asian competitors leverage next-generation agentic workflows.
The Sovereign Alternative: Open Weights as Europe’s Strategic Buffer
Faced with potential withdrawal by proprietary American cloud providers, European industrial conglomerates are increasingly rallying behind open-weight foundation models. By self-hosting open-weight models (such as Mistral Large 4, DeepSeek-V3, and Llama-3.3) within European datacenters, enterprises gain complete operational autonomy.
Self-hosted open-weight architectures allow European banks, automotive manufacturers, and healthcare providers to inspect training code, fine-tune models on proprietary internal records, and maintain full custody over customer data without depending on foreign API endpoints subject to overseas geopolitical decisions.
Recognizing this dynamic, the French and German governments have substantially expanded subsidies for domestic sovereign AI compute clusters, positioning open-weight foundation models as the cornerstone of European technological resilience.
Towards a Pragmatic Synthesis: Technical Conformity and Standardized Auditing
Despite heated public rhetoric, pragmatic negotiators on both sides of the Atlantic are working toward a compromise framework prior to the final statutory enforcement deadline in mid-2027.
The emerging compromise centers on Technical Conformity via Confidential Enclaves. Rather than requiring developers to hand over raw model weights to third-party inspectors, European regulators would accept certified audit reports generated within hardware-encrypted confidential computing enclaves operated under shared international safety standards.
In parallel, standardized SPDX 3.0 AI-Dataset manifests would be adopted to satisfy copyright transparency obligations, allowing developers to verify non-infringement through cryptographic hashes without publicly exposing sensitive proprietary training texts.
Compliance Action Plan: Preparing Multinational AI Architectures for EU Enforcement
Multinational corporations and software vendors operating across transatlantic markets should implement the following compliance measures:
1. Systemic Risk Mapping: Audit internal and third-party foundation models against EU AI Act Article 51 criteria to establish formal risk classification registries.
2. Copyright Provenance Documentation: Maintain machine-readable data bills of materials (AI-BOMs) cataloging training corpora, licensing agreements, and opt-out exclusions.
3. Sovereign Regional Fallbacks: Architect enterprise AI applications with multi-provider routing layers, enabling instant failover to European open-weight models if US cloud APIs face regulatory suspension.
4. Independent Red-Teaming Certifications: Commission pre-deployment red-teaming evaluations from accredited European AI safety testing laboratories.
5. Regulatory Dialogue Engagement: Participate actively in the European AI Office’s ongoing GPAI drafting workshops to provide constructive feedback on technical implementation feasibility.